{{ tourTitle }}
Program overview & self-paced walkthrough
Program overview
Guided walkthrough
{{ stepLabel }}
Restart tour
Certification program
Certify your practice.
Win more business.
The Certified Managed Compliance Provider program gives your MSP the credential, the skills, and the platform mastery to deliver the governance, risk and compliance services your customers are already asking for.
See it from the learner's seat →
{{ ctaLabel }}
Certified Managed Compliance Provider — powered by Digital Hands
Kaseya's only authorized
CMCP certification partner
The market shift
Compliance is no longer a nice-to-have — it is a buying requirement. Your customers face pressure from upstream enterprise clients, cyber-insurance underwriters, and regulators who want proof of a strong security and compliance posture.
The MSPs who deliver compliance credibly — with a structured approach, the right tooling, and a recognized credential — win those engagements. The ones who can't refer them out, or lose them.
01
Grow revenue
New services, better margins
Compliance is among the highest-margin services an MSP can sell — CMCP gives you the skills and credential to charge for it.
02
Earn credibility
A designation customers recognize
The CMCP is awarded to your organization, not an individual — proof that your practice is structured, verified, and audit-ready.
03
Stand out
Differentiate in a crowded market
Most MSPs claim they can do compliance — CMCP-certified MSPs prove it with a recognized credential and platform-aligned skills.
What makes CMCP different
Built for MSPs
Not enterprise teams or internal IT
Gated progression
Prove competency before advancing
Platform-aligned
Maps to Kaseya Compliance Manager
Expandable coverage
Add framework deep-dives as you grow
Organization-level
The business earns it, not one employee
Kaseya exclusive
Kaseya's only authorized CMCP partner
What the certification is
An organization-level designation for your MSP
The CMCP is awarded to your MSP as a business. It signals to every prospect and customer that your practice has been trained, tested, and verified to deliver compliance services using a structured, auditable methodology built on the Kaseya Compliance Manager platform.
01 Delivered via
Self-paced LMS-based program with gated assessments after every module
02 Earned by
Your organization — requires at least one user to complete and pass the full program
03 Built on
Kaseya Compliance Manager, the platform your practice already uses or is investing in
04 Expandable
Add framework-specific, deep-dive modules as your customer base and practice grow
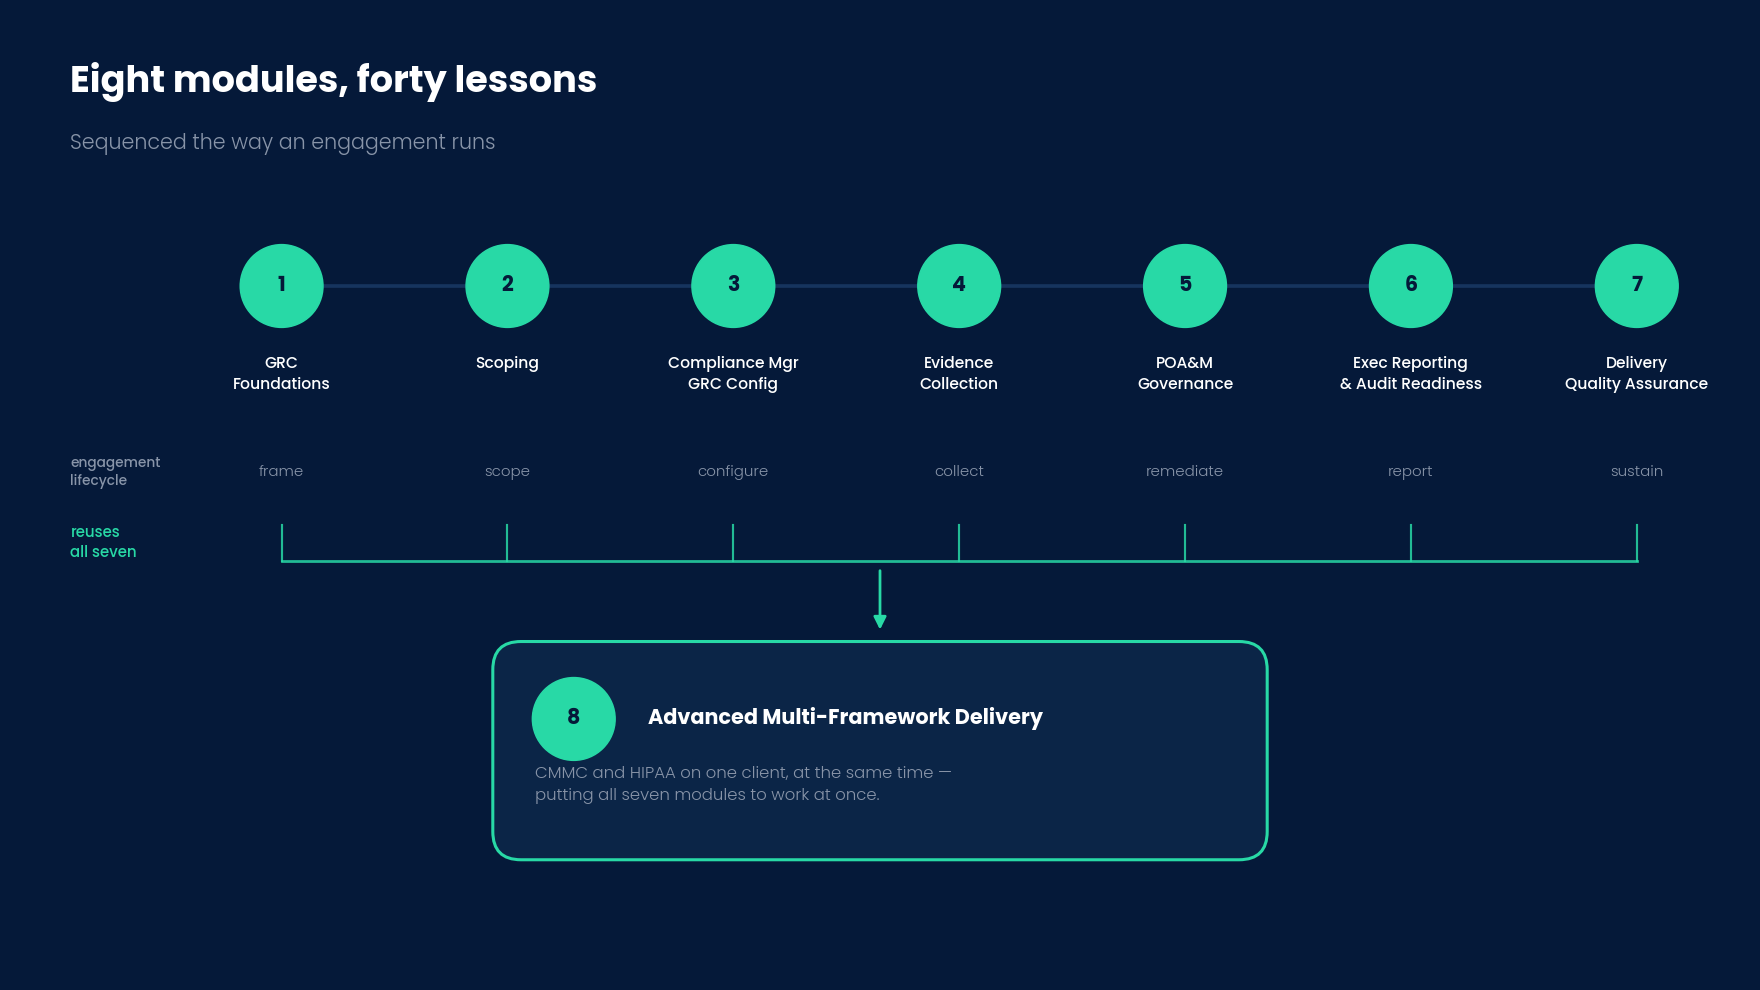
Core certification · modules 1–8
Eight progressive modules build your practice from the ground up — from compliance fundamentals and platform configuration through client delivery, reporting, and advanced multi-framework engagements. Every module is gated: you advance when you can prove you're ready.
01
GRC Foundations
Lead any compliance conversation with confidence: explain what GRC means, why customers care, and your role as their compliance partner.
02
Framework Scoping & Control Mapping
Scope any engagement accurately, map controls across frameworks, and build unified evidence strategies that serve multiple standards at once.
03
Compliance Manager Configuration
Configure Kaseya Compliance Manager for any client: activate frameworks, integrate your tool stack, set role-based access, and validate scans from day one.
04
Evidence Collection & Validation
Collect and package audit-ready evidence that meets auditor standards across automated outputs and manual collection so nothing gets kicked back.
05
POA&M Governance
Run a remediation-tracking program clients can see, understand, and act on — turning compliance gaps into a managed, accountable process.
06
Executive Reporting & Audit Readiness
Produce board-ready reports and auditor-accepted evidence packages to guide clients through the audit itself without surprises.
07
Delivery QA & Continuous Governance
Operate with consistent quality: detect drift between audit cycles, score your own delivery, and keep every client on track.
08
Advanced Framework Delivery
Handle the most complex engagements — multi-framework clients, CMMC and HIPAA nuances, overlapping evidence — with depth and precision.
The CMCP designation is awarded once all modules are complete and every certification gate is passed.
Go further with Module X
sold separately
Once you have earned your CMCP designation, each Module X lesson delivers practitioner-level mastery of a single framework — well beyond the core program's foundational coverage. Purchase individual lessons for the frameworks your customers need most.
X.1
CMMC Level 1
17 practices, FAR 52.204-21, SPRS scoring, self-assessment methodology.
X.2
CMMC Level 2
110 practices, NIST SP 800-171, C3PAO prep, CUI scoping, SSP development.
X.3
NIST CSF 2.0
All six core functions including Govern, profile development, gap analysis.
X.4
ISO/IEC 27001:2022
93 Annex A controls, ISMS clause structure, Statement of Applicability.
X.5
CIS Controls v8
18 Controls, 153 Safeguards, Implementation Groups 1–3, tool-stack alignment.
X.6
SOC 2 (Type I & II)
Trust Services Criteria, evidence sourcing, sampling standards, report interpretation.
X.7
HIPAA Security & Privacy
Required and addressable safeguards, ePHI detection, risk analysis, BAAs, breach notification.
Why Digital Hands
Digital Hands is a cybersecurity and risk-advisory firm specializing in managed security, Unified Security Posture Management, and comprehensive risk management services. We built the CMCP program after seeing what happens when MSPs deliver compliance without a structured foundation — inconsistent delivery, unhappy clients, and missed revenue.
CMCP is not a generic GRC course. It is purpose-built for MSPs in the Kaseya ecosystem, aligned to the Kaseya Compliance Manager platform, and designed by practitioners who deliver these services every day.
Ready to earn your CMCP designation?
The CMCP program is available exclusively through Digital Hands in partnership with Kaseya.
Walk through the learner experience →
Mail
Inbox · 12
Flagged
Sent
Clients
Archive
FW: Assessment evidence request — response required
••
████████ (client contact)
·
to you@yourfirm.com
·
08:14
Our assessor sent the evidence list this morning. I told them you handle our security program, so I am forwarding it straight to you. Let me know what you need from our side.
41
items requested
14
days to respond
?
framework scoped
1. Current system security plan, including boundary diagram and asset inventory
2. Access control policy with review evidence for the trailing four quarters
3. Audit log retention configuration and sample extract
4. Incident response plan plus most recent tabletop record
5. Media sanitisation procedure and disposal certificates
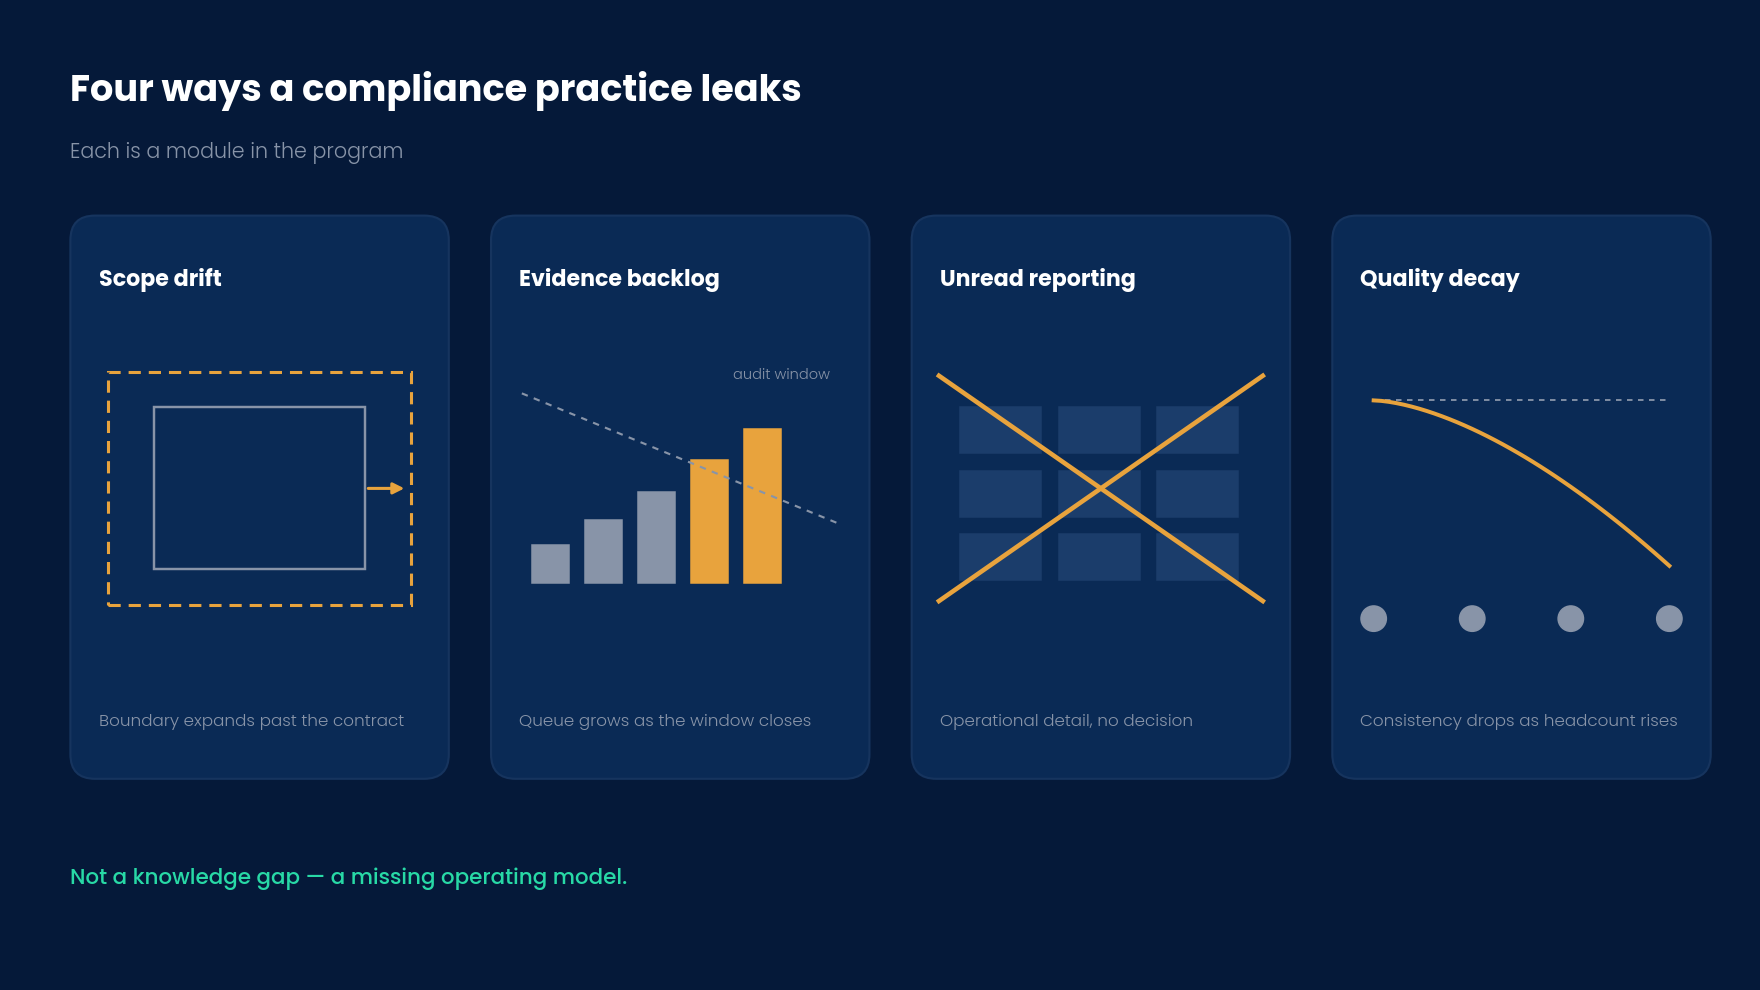
Four ways a compliance practice leaks Eight modules, forty lessons
CMCP Learning Portal
Curriculum
Field Guides
Assessment
AJ
Enrolled program
Certified Managed
Compliance Provider
11 of 40 lessons complete
Overview
Modules
Field Guides
Final exam
Credential
Welcome back, Alex
Self-paced · you set the pace, the gates set the order
Ask the Expert
Next up
Module 4 · Lesson 3 — Drawing a defensible sample
11 min video · field guide attached · 2 of 5 lessons done in this module
Resume lesson
1
GRC Foundations
5 lessons · complete
2
Framework Scoping & Control Mapping
5 lessons · complete
3
Compliance Manager Configuration
5 lessons · gate passed
4
Evidence Collection & Validation
5 lessons · in progress
5
POA&M Governance
Locked · pass the Module 4 gate
6
Executive Reporting & Audit Readiness
Locked · pass the Module 5 gate
7
Delivery QA & Continuous Governance
Locked · pass the Module 6 gate
8
Advanced Framework Delivery
Capstone · locked until Module 7
Module 4 · Evidence Collection & Validation
/
Lesson 3 — Drawing a defensible sample
Lesson 3 of 5
Now playing
Define the population before you draw
CC · English
❙❙
04:12 / 11:38
·
1.25×
Chapter 2 of 4 — Reconciling the population
DOCX
Module 4 Field Guide
XLSX
Sample worksheet
PDF
Lesson slides
Transcript
auto-scroll
03:41
So the assessor has asked for four quarters of access reviews across every in-scope account.
04:06
Before you draw anything, you have to say out loud what the population is — and write it down.
04:22
An export the client sent you is not a population. It is a file. Reconcile it against the directory first.
04:48
Auditors rarely challenge your sample size. They challenge the boundary you drew it from.
Lesson notes and bookmarks stay with your account across sessions.
Module 4 knowledge check
· question 3 of 8
Gate: 80% to advance
A client sends you an exported list of 340 accounts and asks you to sample 25 of them for access-review evidence. What do you do first?
A
Draw 25 accounts at random from the exported list and document the method.
B
Reconcile the export against the in-scope directory, then draw the sample.
C
Ask the client which 25 accounts they would prefer you review.
D
Request all 340 access reviews so the sample cannot be challenged.
{{ feedbackLabel }}
{{ feedbackText }}
This module's gate
Module 4 assessment
8 questions
3 of 8 answered
✓
Modules 1–3 gates passed
Module 4 gate in progress
Module 5 locked
Score below 80% and the module reopens for review before you can retake the gate.
Every module ends in a gate. The designation is awarded only when all eight are passed.
Module 4 · Evidence Collection & Validation
/
Lesson 3 — Drawing a defensible sample
Progression
✓
Frame the request
✓
Define the population
Draw the sample
Test for sufficiency
Package for the assessor
Attached
Module 4 Field Guide
Sample worksheet .xlsx
Objective
An assessor asks for four quarters of access reviews across 340 accounts. Draw a sample you can defend when they push back on it.
A sample is defensible when the population is defined before the draw, the method is stated, and the exclusions are written down. Auditors rarely challenge the size. They challenge the boundary.
Common mistake
Pulling the sample from the account list the client happened to export.
What's right
Reconcile the population to the in-scope directory first, then draw.
Capability outcome
Draw and document a sample that survives assessor challenge.
Submit deliverable
Kaseya Compliance Manager
Scope configuration
Simulated tenant
Scope
Frameworks
Evidence
Roles
Baseline
Scope structure
▾ Client environment
▾ CUI enclave
Identity & directory
File services
Endpoints — 42
▾ Out of scope
Guest network
Marketing SaaS
Boundary is defined once and every framework citation resolves against it.
Framework activation
CMMC Level 2
HIPAA Security Rule
SOC 2
ISO 27001
Role alignment
Provider — configure, review
Client owner — attest
Assessor — read only
Baseline scan — inherited tenant
116 checks
Audit log retention — 12 months
MFA enforced on privileged roles
Guest network inherited as in-scope
Previous provider's assumption conflicts with the boundary defined at left. Verify before you accept the tenant.
Evidence automation — not configured
Configure
Verify against scope
Simulated interface · Module 3 is hands-on and requires Kaseya Compliance Manager tenant access
Module 2 Field Guide · Scoping
Decision table 2.3
Boundary calls that go wrong most often
What's wrong
What's right
Why
Scope the whole network because the client asked for "full coverage".
Scope the enclave that stores or processes the regulated data.
Overruns are absorbed by you, not the client.
Accept the asset inventory the client provides.
Reconcile the inventory against directory and network data.
Unlisted assets become findings with your name on them.
Exclude a system verbally during the kickoff call.
Record every exclusion with its rationale in the scope document.
An undocumented exclusion reads as an omission.
Named mistake
"Coverage creep" — see scenario 2.
Scenario 1 · clean
page 2 of 2
A 60-person manufacturer, one contract, one enclave
The client holds a single prime contract with a CUI flow-down clause. Engineering drawings arrive by SFTP and live in one file share. Everyone else in the business works in a separate tenant.
You have two defensible boundaries available: the file share alone, or the file share plus the six engineering workstations that open the drawings. The second is larger and it is the correct one, because the drawings are cached locally after every open.
Write the exclusion for the rest of the estate before the client asks for it. When the assessor tests the boundary in month nine, the document already answers the question.
Deliverable
A one-page scope boundary with three named exclusions and the cache rationale.
Scenario 2 — the same client, after an acquisition — goes sideways.
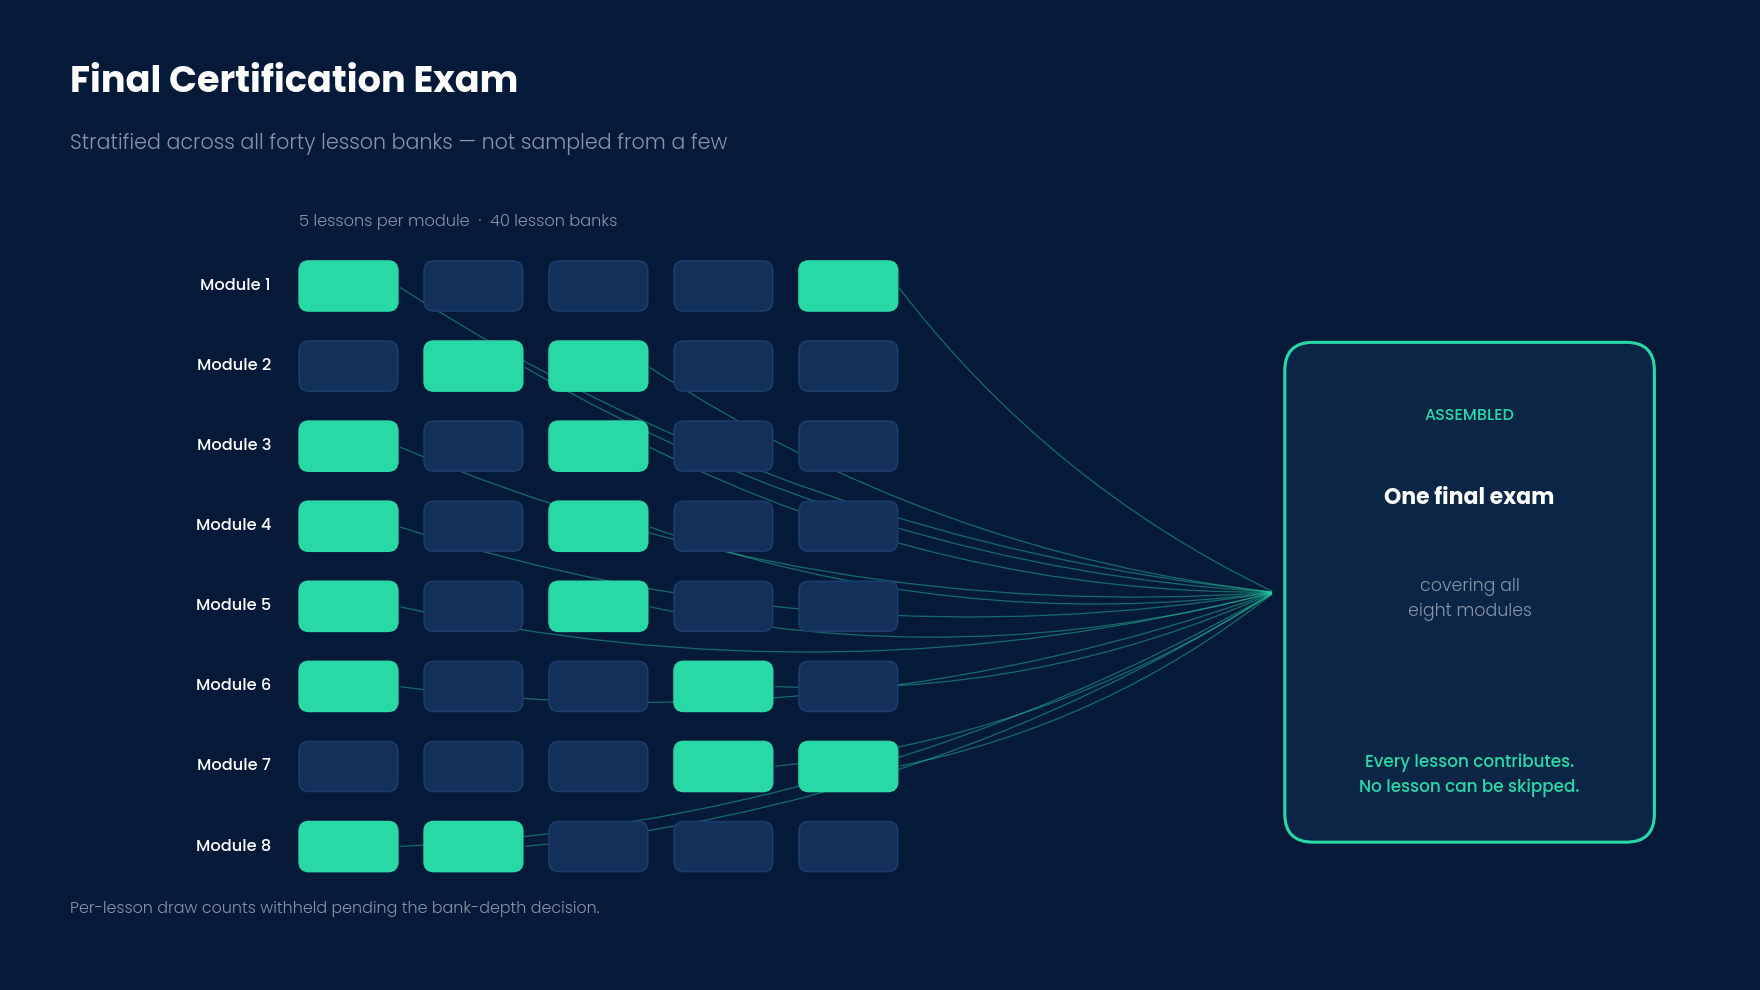
Final certification exam, stratified across all forty lesson banks
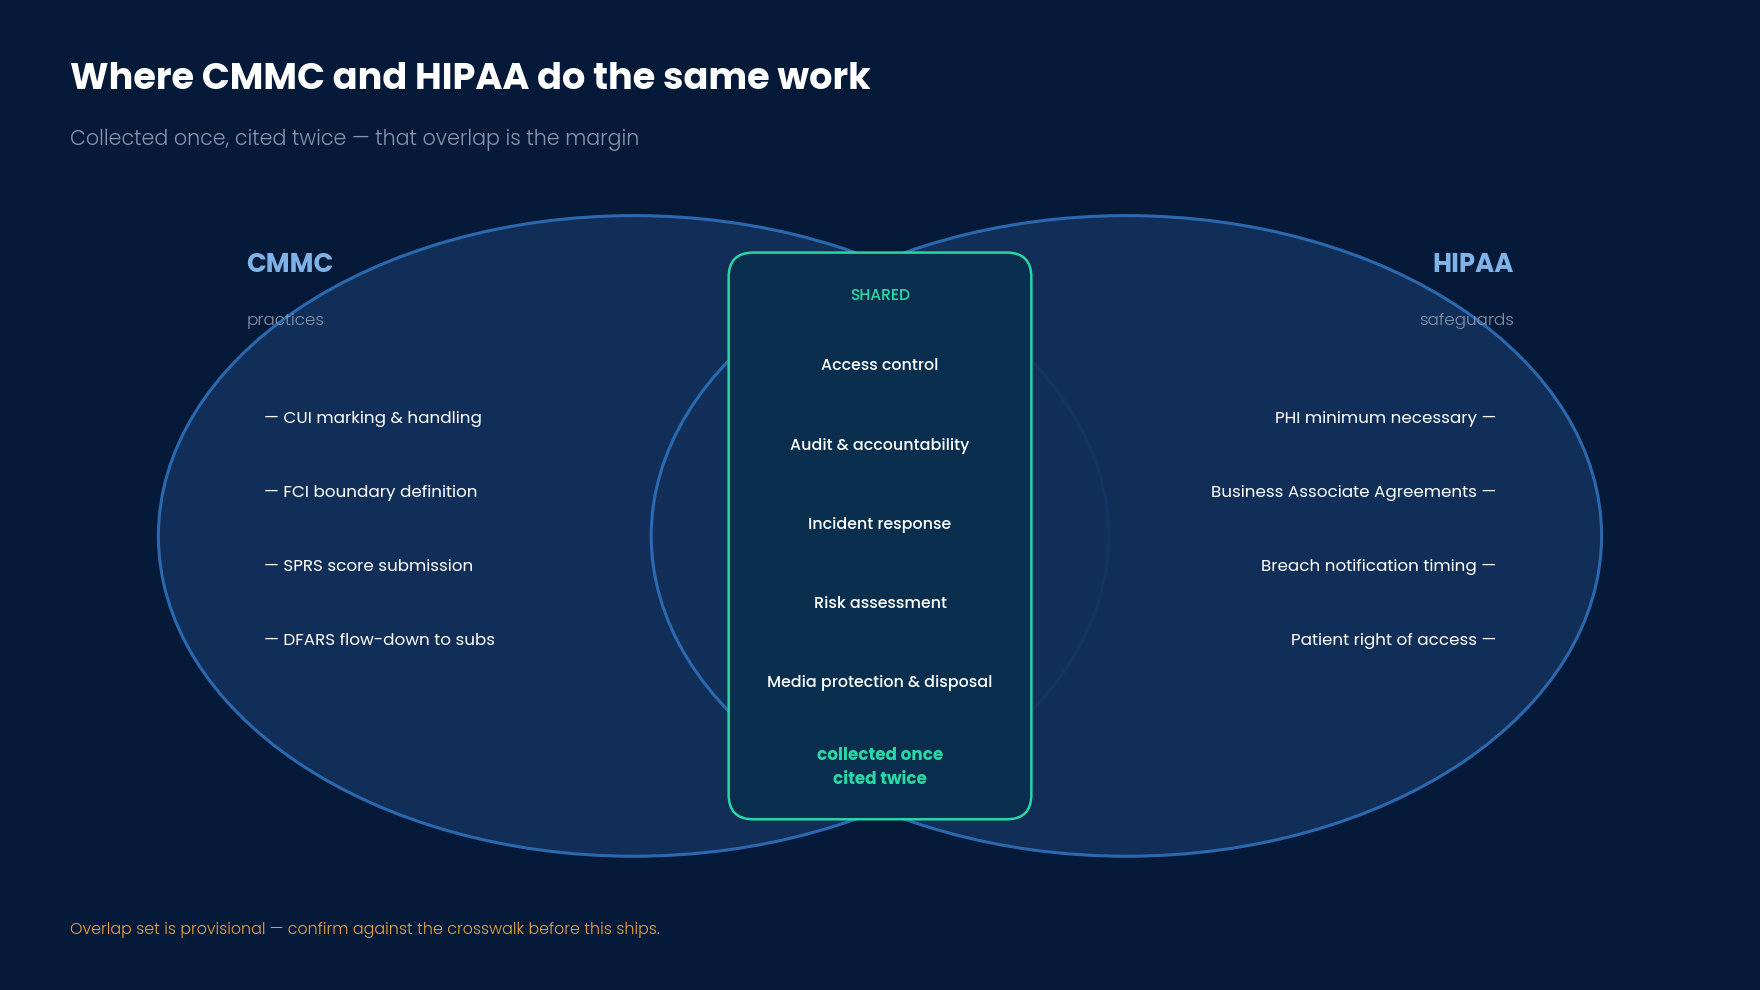
Where CMMC and HIPAA do the same work
Control · Account management
1 scope
Satisfies
CMMC AC.L2-3.1.1
HIPAA §164.312(a)(1)
Evidence artifacts collected
1
Awarded on completion
Organization designation
Certified Managed Compliance Provider
Your Firm, LLC
How it was earned
AJ
Alex Jordan completed all eight modules, passed every gate, and passed the knowledge exam.
The designation belongs to the business, not the employee — it stays with the practice, and additional staff can be licensed onto the same program.
Credential verification
verify.digitalhands.com
✓
Assertion valid
Organization
Your Firm, LLC
Issuer
Digital Hands
Issued
14 March 2026
Assessment
8 module gates + knowledge exam
Designation ID
CMCP-2026-0417
Maintained by
Annual recertification exam
Eight modules.
Forty lessons.
One operating model.
{{ ctaLabel }}
Module 3 is hands-on and requires Kaseya Compliance Manager tenant access.
Certified Managed Compliance Provider — powered by Digital Hands
{{ chapter }}
{{ stepLabel }}
{{ title }}
{{ body }}
{{ detail }}
{{ detailLabel }}
Back
{{ nextLabel }}
Click the highlighted area, use ← → , or jump with the dots