MANAGED SECURITY OPERATIONS
24/7 detection and response across your endpoints, identities, cloud, SaaS, and network — delivered 24/7 by US-based analysts inside the CyGuard® Portal. Speed and automation where it counts, customization and expertise where a one-size-fits-all solution falls short.
WHAT WE DELIVER
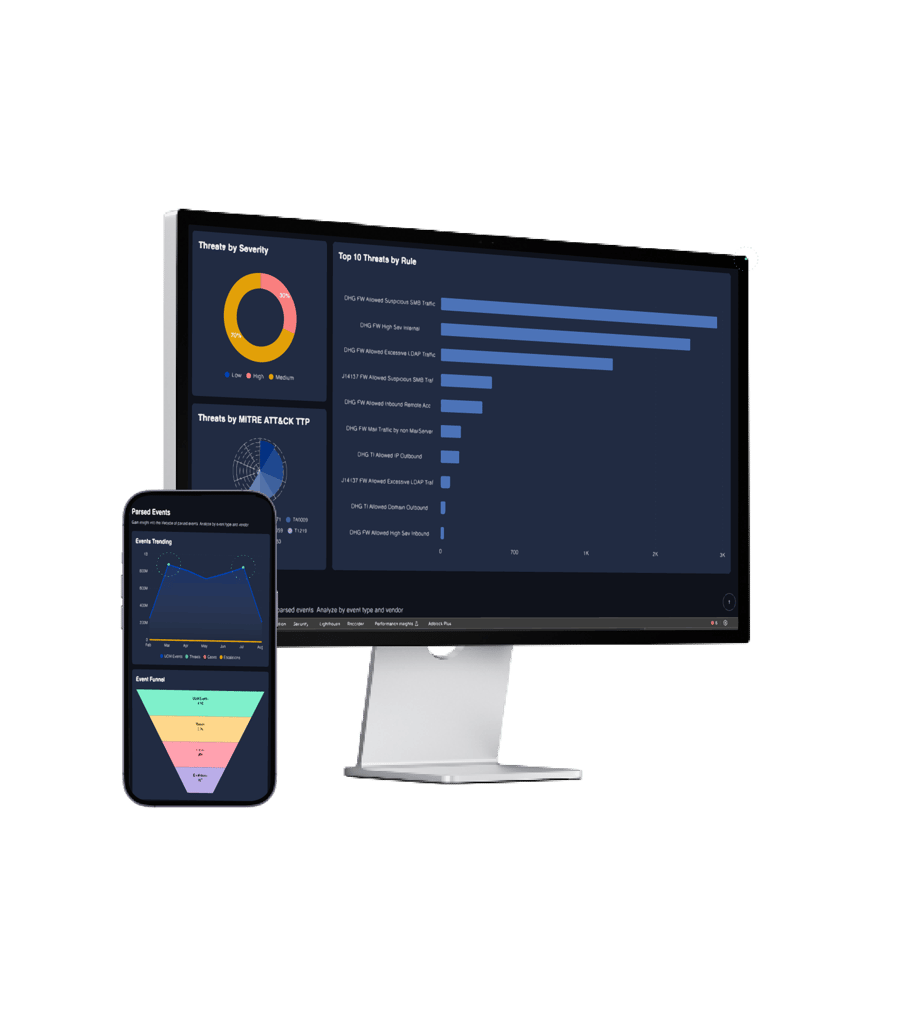
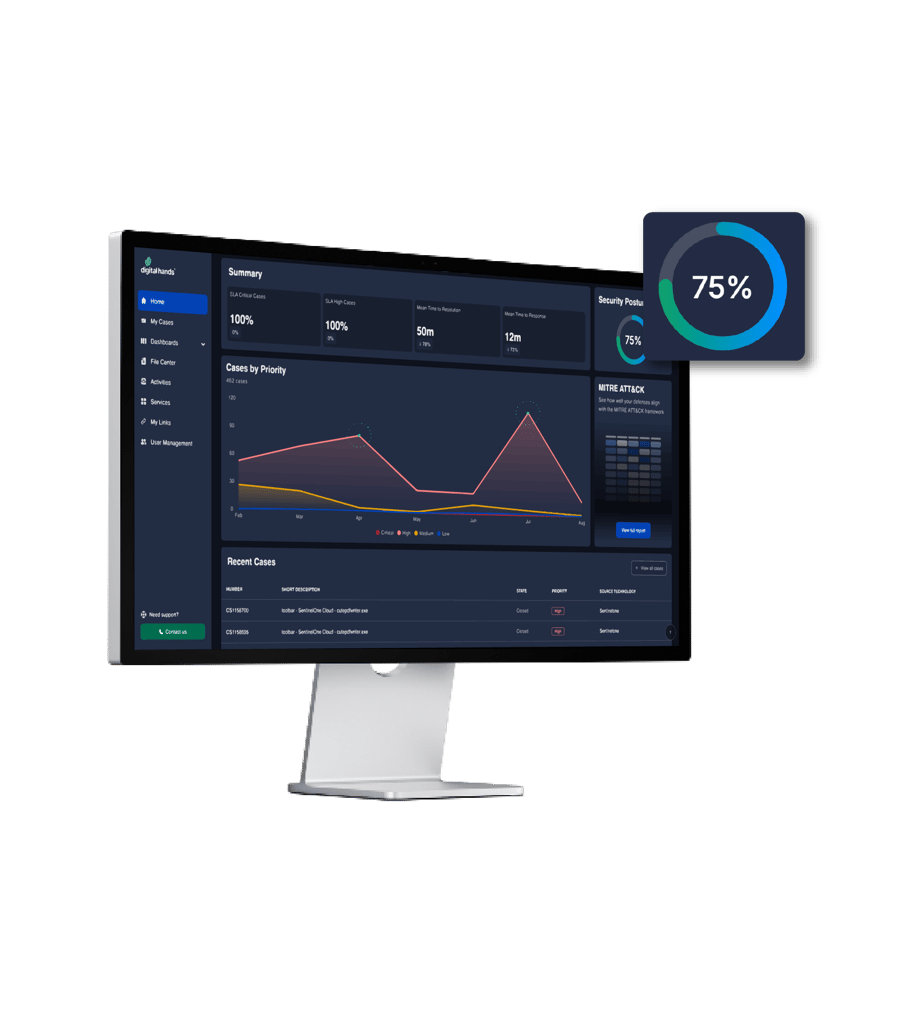
Real-time intelligence, coordinated response, and a platform tailored to the environment you actually operate. The CyGuard Portal is where it all comes together — single-pane visibility from SIEM, EDR, identity, cloud, and the firewalls between them.
attacks target organizations each week on average¹
or less for an attacker to move laterally through a network²
on average to identify a breach without managed detection and response³
REAL-TIME INTELLIGENCE
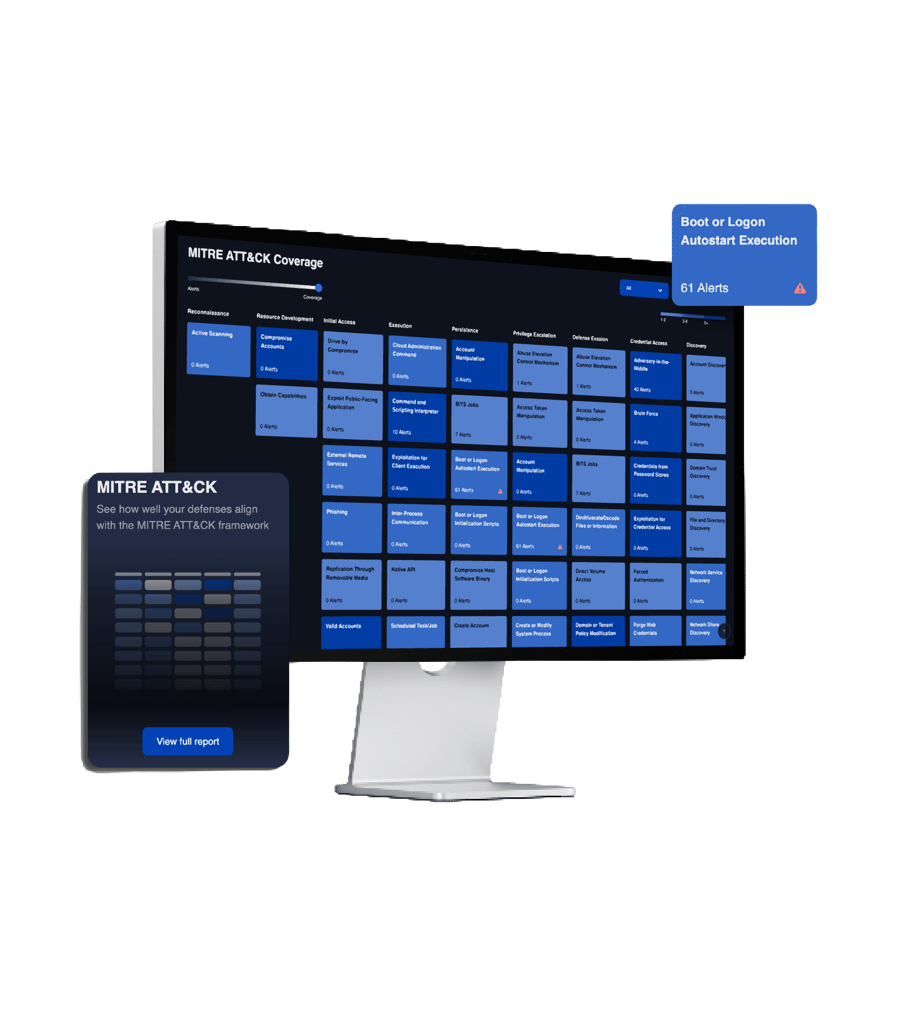
Mapped to MITRE ATT&CK and enriched with the context our analysts have built across years of incident response, the portal shows you what is happening and why — not just what fired.
COORDINATED RESPONSE
Every second of dwell time matters. Automated playbooks combined with human expertise contain threats across SIEM, EDR, identity, and firewall — from one place, with full audit trail.
TAILORED TO YOUR ENVIRONMENT
One-size-fits-all MDR makes you adapt to the vendor. MDR adapts to you — with custom detections, parsers, and playbooks built around the tooling you already operate, and live posture visibility on top.
FAQS
The questions buyers ask us most about Managed Detection & Response — answered directly.
MDR is security operations that don’t wait for attacks to happen. We pair experienced analysts with the CyGuard Maestro™ security fabric to find and stop threats before they hurt your business — actively hunting 24/7, not just monitoring for alarms.
Yes — with real experts, not a call center. You get a dedicated team that knows your environment and is available 24/7. When you need help, you talk directly to the analysts who can act.
We act on it immediately. You’ll see exactly what is happening, where, and what we are doing about it — in real time, inside the CyGuard Portal, with clear updates and decisive action.
Yes — fast. The moment we identify a threat, we can isolate affected hosts and users to stop the spread. You see every step and remain in control of the response.
Continuous threat hunting 24/7. Smart filtering that cuts through the noise to surface real threats. Custom response playbooks tailored to your environment. Automated containment at machine speed. Regular strategy reviews that strengthen the program. And clear reporting that demonstrates ROI to your leadership.
Book an intro call. We’ll scope the engagement, review the environment, and propose a path forward — typically starting with a Security Posture Assessment so the MDR program is informed by your actual exposure on day one.
Co-managed, technology-agnostic SIEM with 200+ custom detections and continuous tuning across Splunk, Sentinel, Google SecOps, CrowdStrike, Securonix, and QRadar.
ExploreEndpoint detection and response — deployed, tuned, and monitored continuously across the full device estate.
ExploreRound-the-clock US-based security and network operations from the same trusted team.
Explore